
 dinero_admin
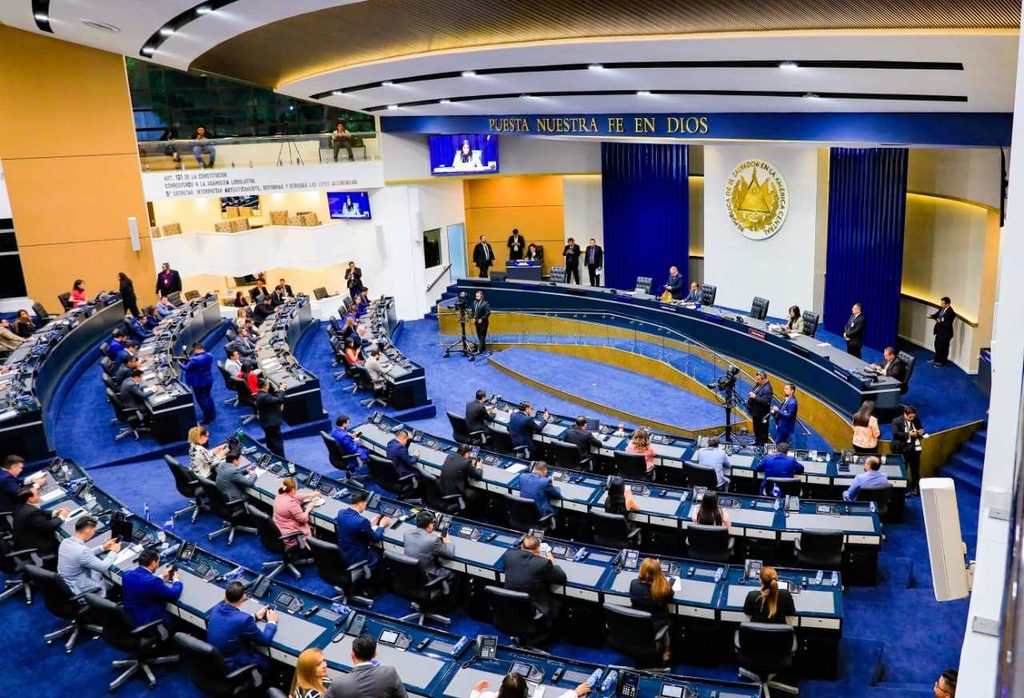
The Legislative Assembly voted 57–0 to amend the Personal Data Protection Law, altering the procedures by which individuals may request access to, correction of, deletion of, or other actions regarding their personal data. According to lawmakers, these changes aim to facilitate the exercise of these rights and allow institutions, companies, and organizations to manage requests in a manner consistent with their internal structures.
Current regulations designate the data protection officer as the person responsible for upholding ARCO-POL rights (Access, Rectification, Cancellation, Opposition, Portability, the Right to be Forgotten, and Limitation). However, under the reforms, individuals will be able to submit requests to consult, correct, delete, or exercise other rights regarding their information directly to the institution, company, or organization holding or using their personal data.
Nuevas Ideas legislator Dania González explained that the amendments would streamline the implementation of the Personal Data Protection Law without altering the rights and guarantees it grants to citizens.
For public institutions, the requirement to appoint a data protection officer remains mandatory. The reform stipulates that this role may be filled by the institution’s existing Information Officer.
González further stated that the Agencia de Ciberseguridad del Estado (ACE) will retain its oversight authority and its supervisory, control, and inspection functions as established by law. Additionally, a Director of Personal Data Protection position will be created; this official will assist the ACE Director General and handle administrative sanctioning proceedings.
“In short, we are preserving the rights, the guarantees, and the authority of oversight; what we are modernizing is the compliance mechanism. Why? Because the reform means less administrative rigidity, greater institutional efficiency, and the same level of personal data protection for all salvadorans”, the legislator said.
The reforms also regulate the processes for correcting information. Regulations stipulate that when a person requests the rectification of their data, a record must be made indicating that the information is undergoing rectification while the request is being processed.
Furthermore, if the data has already been shared with other individuals or entities, the obligated party must provide notification of the correction, update, or deletion within five business days of determining that the request is valid. Similarly, a five-business-day deadline is established for handling requests in which a person withdraws their consent for the processing of their personal data.
You may also read: